Security
The 4.52 release includes security improvements and fixes across EBS. Review the tables below to identify which products are affected and whether you need to take any action.
The information is divided into:
-
Security updates: security-related changes and improvements.
-
Fixed security issues: vulnerabilities resolved in this release.
Security updates
The following table lists the security-related changes and improvements included in this release.
| Module | Change | What this means for you | Affected topics |
|---|---|---|---|
|
Central, Shape, and Ontrack. |
EBS password security update |
Over 5 years ago, EBS authentication was updated to use a stronger password protection mechanism. The less secure method was left in place so that existing passwords continued to work following the upgrade. The stronger mechanism was applied the next time a password was changed. In this release, to improve product security, we have retired the older method. Anyone still using it will be asked to set a new password the next time they sign in to Ontrack, Shape or Central. This is a one-time step and will happen automatically.
Most people won't notice anything. Only accounts still on the older password method are affected (i.e. accounts where the password hasn't been updated for many years); everyone else signs in exactly as before. If the forgotten password route is available, a message will be shown explaining that the user needs to reset their password. If the forgotten password route is not available, the user will be advised to contact an administrator to reset their password on their behalf. The forgotten password process and screens have not been modified in this release. |
Not applicable |
|
Ontrack |
Ontrack X-XSS-Protection header removed |
The X-XSS-Protection header has been removed from Ontrack responses. This is a deprecated header that provides no security benefit in modern browsers, having been superseded by the Content Security Policy (CSP). |
Not applicable |
|
Ontrack |
Improved security across Ontrack |
We’ve upgraded the Angular technology used across Ontrack manager, FES return, interview manager, GRIDS and CHARTS. These upgrades help protect your data, resolve known security findings and maintain compliance with current support and security requirements. You can continue to use the affected screens and features as usual. You will see no changes to their appearance, behaviour, or functionality. |
Not applicable |
|
Central |
EBS Central Learner Details Ontrack tab (and CefSharp embedded browser) removed |
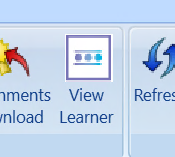
In EBS Central, the Ontrack tab has been removed and replaced with a ribbon item View Learner which opens Learner details in Ontrack Hub in your default browser. The visibility of this button is controlled by the existing Show Ontrack in Central Learner details institution setting.
This change is part of a wider security-led change to remove the embedded CefSharp browser from EBS Central. As this browser was bundled with EBS releases it did not receive timely security updates and was the root cause of several functionality defects in the Ontrack tab. With its removal, web functionality in EBS Central has either been replaced (e.g. Ontrack Learner Details tab), or now uses the evergreen version of WebView2, which is an up-to-date version of Chromium which receives regular platform updates and security patches from Microsoft. WebView2 is pre-installed on all Windows 11 devices (and most active Windows 10 devices) and can be installed on any supported Windows Operating System that supports Microsoft Edge. Embedded staff MOTO payments have also been switched from using CefSharp to WebView2 if the institution setting The method of transfer that ebs: central uses for ePayments is configured as Display payment in popup window. |
|
|
Central |
Central grid option to export to Excel 97-2003 (.XLS) Format has been removed |
The option to export Central grid data to "Excel 97-2003 (.XLS) Format" has been removed. The default option will now be Excel 2007+ (.XLSX) Format. This change helps protects your data, since this legacy format lacks the security and encryption support of modern Excel formats and is no longer maintained by Microsoft. |
|
|
Ontrack and REST services. |
Ontrack output sanitisation |
This release strengthens the security of Ontrack by introducing platform-wide output sanitisation: automatically cleaning content before it is displayed, so that harmful or unintended code cannot be included in what users see. What's changed?
Impact for users No change to normal day-to-day use. Free-text fields work as before, now with more consistent protection. |
Not applicable |
Fixed security issues
The following table lists the security issues resolved in this release.
| Module | Issue summary | Resolution | Found in | Incident number | Affected topics |
|---|---|---|---|---|---|
| Ontrack and REST services. | A vulnerability in an HTML sanitisation library could allow an attacker to bypass sanitisation by using a specially crafted template tag. This could result in unsafe HTML being processed by an affected application. CVE-2026-25543. | The vulnerability has been resolved by upgrading the affected libraries. | Not applicable | Not applicable | Not applicable |
| Ontrack | A recent penetration test identified a prototype pollution vulnerability in the version of Chart.js used by Ontrack Learner Hub. An attacker could potentially manipulate JavaScript object properties and affect application behaviour. CVE-2020-7746. | The vulnerability has been resolved by upgrading the affected Chart.js library. | Not applicable | Not applicable | Not applicable |
|
Central, Shape, and Ontrack. |
An XML external entity (XXE) vulnerability was identified in the log4net logging library used by all EBS modules. If exploited, it could allow an attacker to interfere with XML processing and potentially access data or system resources. CVE-2018-1285. | The vulnerability has been resolved by upgrading the affected log4net library. | Not applicable | Not applicable | Not applicable |
| Ontrack | A prototype pollution vulnerability was identified in the Swiper library used by the ILP Learner Angular application. An attacker could potentially manipulate JavaScript object properties and affect application behaviour. CVE-2026-27212. | The vulnerability has been resolved by removing the affected Swiper library from the application. | Not applicable | Not applicable | Not applicable |
| Ontrack | A mutation cross-site scripting (mXSS) vulnerability was identified in the AngleSharp library used by Ontrack. Under specific conditions, unsafe HTML could be modified after sanitisation and potentially allow a malicious script to run in a user’s browser. CVE-2026-54570. | The vulnerability has been resolved by upgrading the affected AngleSharp library. | Not applicable | Not applicable | Not applicable |
| Ontrack | An uncontrolled resource consumption vulnerability was identified in the Braces library used by Ontrack Safeguarding. Processing specially crafted input could consume excessive system resources and affect service availability. CVE-2024-4068. | The vulnerability has been resolved by upgrading the affected libraries. | Not applicable | Not applicable | Not applicable |
| Central | A STARTTLS response injection vulnerability was identified in the EBS email integration. Under specific conditions, a malicious or compromised mail server could potentially manipulate the connection upgrade process and affect the security of email communications. CVE-2026-41319. | The vulnerability has been resolved by upgrading the affected libraries. | Not applicable | Not applicable | Not applicable |
| Central | A carriage return and line feed (CRLF) injection vulnerability was identified in the EBS email integration. Specially crafted input could potentially inject additional content into an email message or its headers. CVE-2026-30227. | The vulnerability has been resolved by upgrading the affected libraries. | Not applicable | Not applicable | Not applicable |
| Ontrack | A denial-of-service vulnerability was identified in a .NET library used by Ontrack. Processing specially crafted input could cause excessive resource consumption and affect service availability. CVE-2026-26127. | The vulnerability has been resolved by upgrading the affected libraries. | Not applicable | Not applicable | Not applicable |
| Ontrack Learner/Staff Hub - install package | Penetration testing found that some internal development files were left in your Ontrack Learner Hub and Staff Hub installation and could be discovered on the web server by anyone. | The upgrade process now removes these internal files from your Ontrack Learner/Staff Hub installation, so they're no longer deployed or publicly accessible. | 4.49 | 1805002 | Not applicable |
| Ontrack - Correspondence Manager / Report Viewer | Penetration testing found that certain Correspondence Wizard fields in Ontrack Hub, and the reportid parameter on the Report Viewer page, weren't fully validated — crafted input could trigger an unhandled SQL error. | Correspondence Wizard input (for example, address and footer fields) is now sanitised against embedded HTML or script, and an invalid Report Viewer reportid now returns a clean error instead of an unhandled exception. | 4.49 | 1811388 | Not applicable |
| Ontrack Learner Hub | Penetration testing found that script entered into a qualification description on the 'Add Qualifications' page in Learner Hub was stored without being sanitised. | Input to the qualification description field is now sanitised, so stored script can no longer be retained or executed. | 4.49 | 1830535 | Not applicable |
| Ontrack - Correspondence Manager | Penetration testing found that processing a correspondence template could cause the server to contact external domains that weren't on your institution's approved image list. | Correspondence processing now only allows images from domains on your institution's approved list, removing the external lookup. | 4.49 | 1811387 | What is correspondence manager? |
| Intel - Business Intelligence (pi / Power BI embed) | Security scanning found the EBS Intel component running an outdated third-party library with a known critical vulnerability. | We've upgraded the EBS Intel (pi) module to a later version, which includes a patched version of the library and closes the vulnerability. | 4.51 | 1868643 | Not applicable |